GRC Artifact Index
Find the right page for your regulation, framework, or control program. Filter by topic, search by keyword, and open the artifact that matches your scope.
Explore artifacts
FIPS 140-3 Implementation Guide
Define the cryptographic module boundary, security level, approved services, operating environments, laboratory testing, and CMVP validation evidence.
FIPS Cryptographic Algorithms Guide
Choose FIPS algorithms and separate algorithm approval, CAVP testing, CMVP module validation, approved use, transitions, and procurement evidence.
NIST CSF 2.0 Implementation Guide
Apply the six NIST CSF 2.0 Functions, Current and Target Profiles, Tiers, implementation examples, evidence, and action planning.
NIST SP 800-161 Rev. 1 C-SCRM Guide
Build cybersecurity supply chain risk management across enterprise governance, acquisition, engineering, operations, suppliers, and system lifecycles.
NIST SP 800-218 SSDF Implementation Guide
Risk-tailored SSDF v1.1 guidance for software producers and acquirers across PO, PS, PW, RV, evidence, supplier assurance, and vulnerability response.
NIST SP 800-53 Rev. 5 Controls Guide
Plain-language guidance for selecting and tailoring NIST SP 800-53 Rev. 5 controls, assigning common and system-specific responsibility, assessing with SP 800-53A, and managing evidence and findings.
NIST SP 800-61 Rev. 3 Incident Response Guide
Plan incident roles, playbooks, communications, evidence, recovery, and legal overlays across the NIST SP 800-61 Rev. 3 and CSF 2.0 lifecycle.
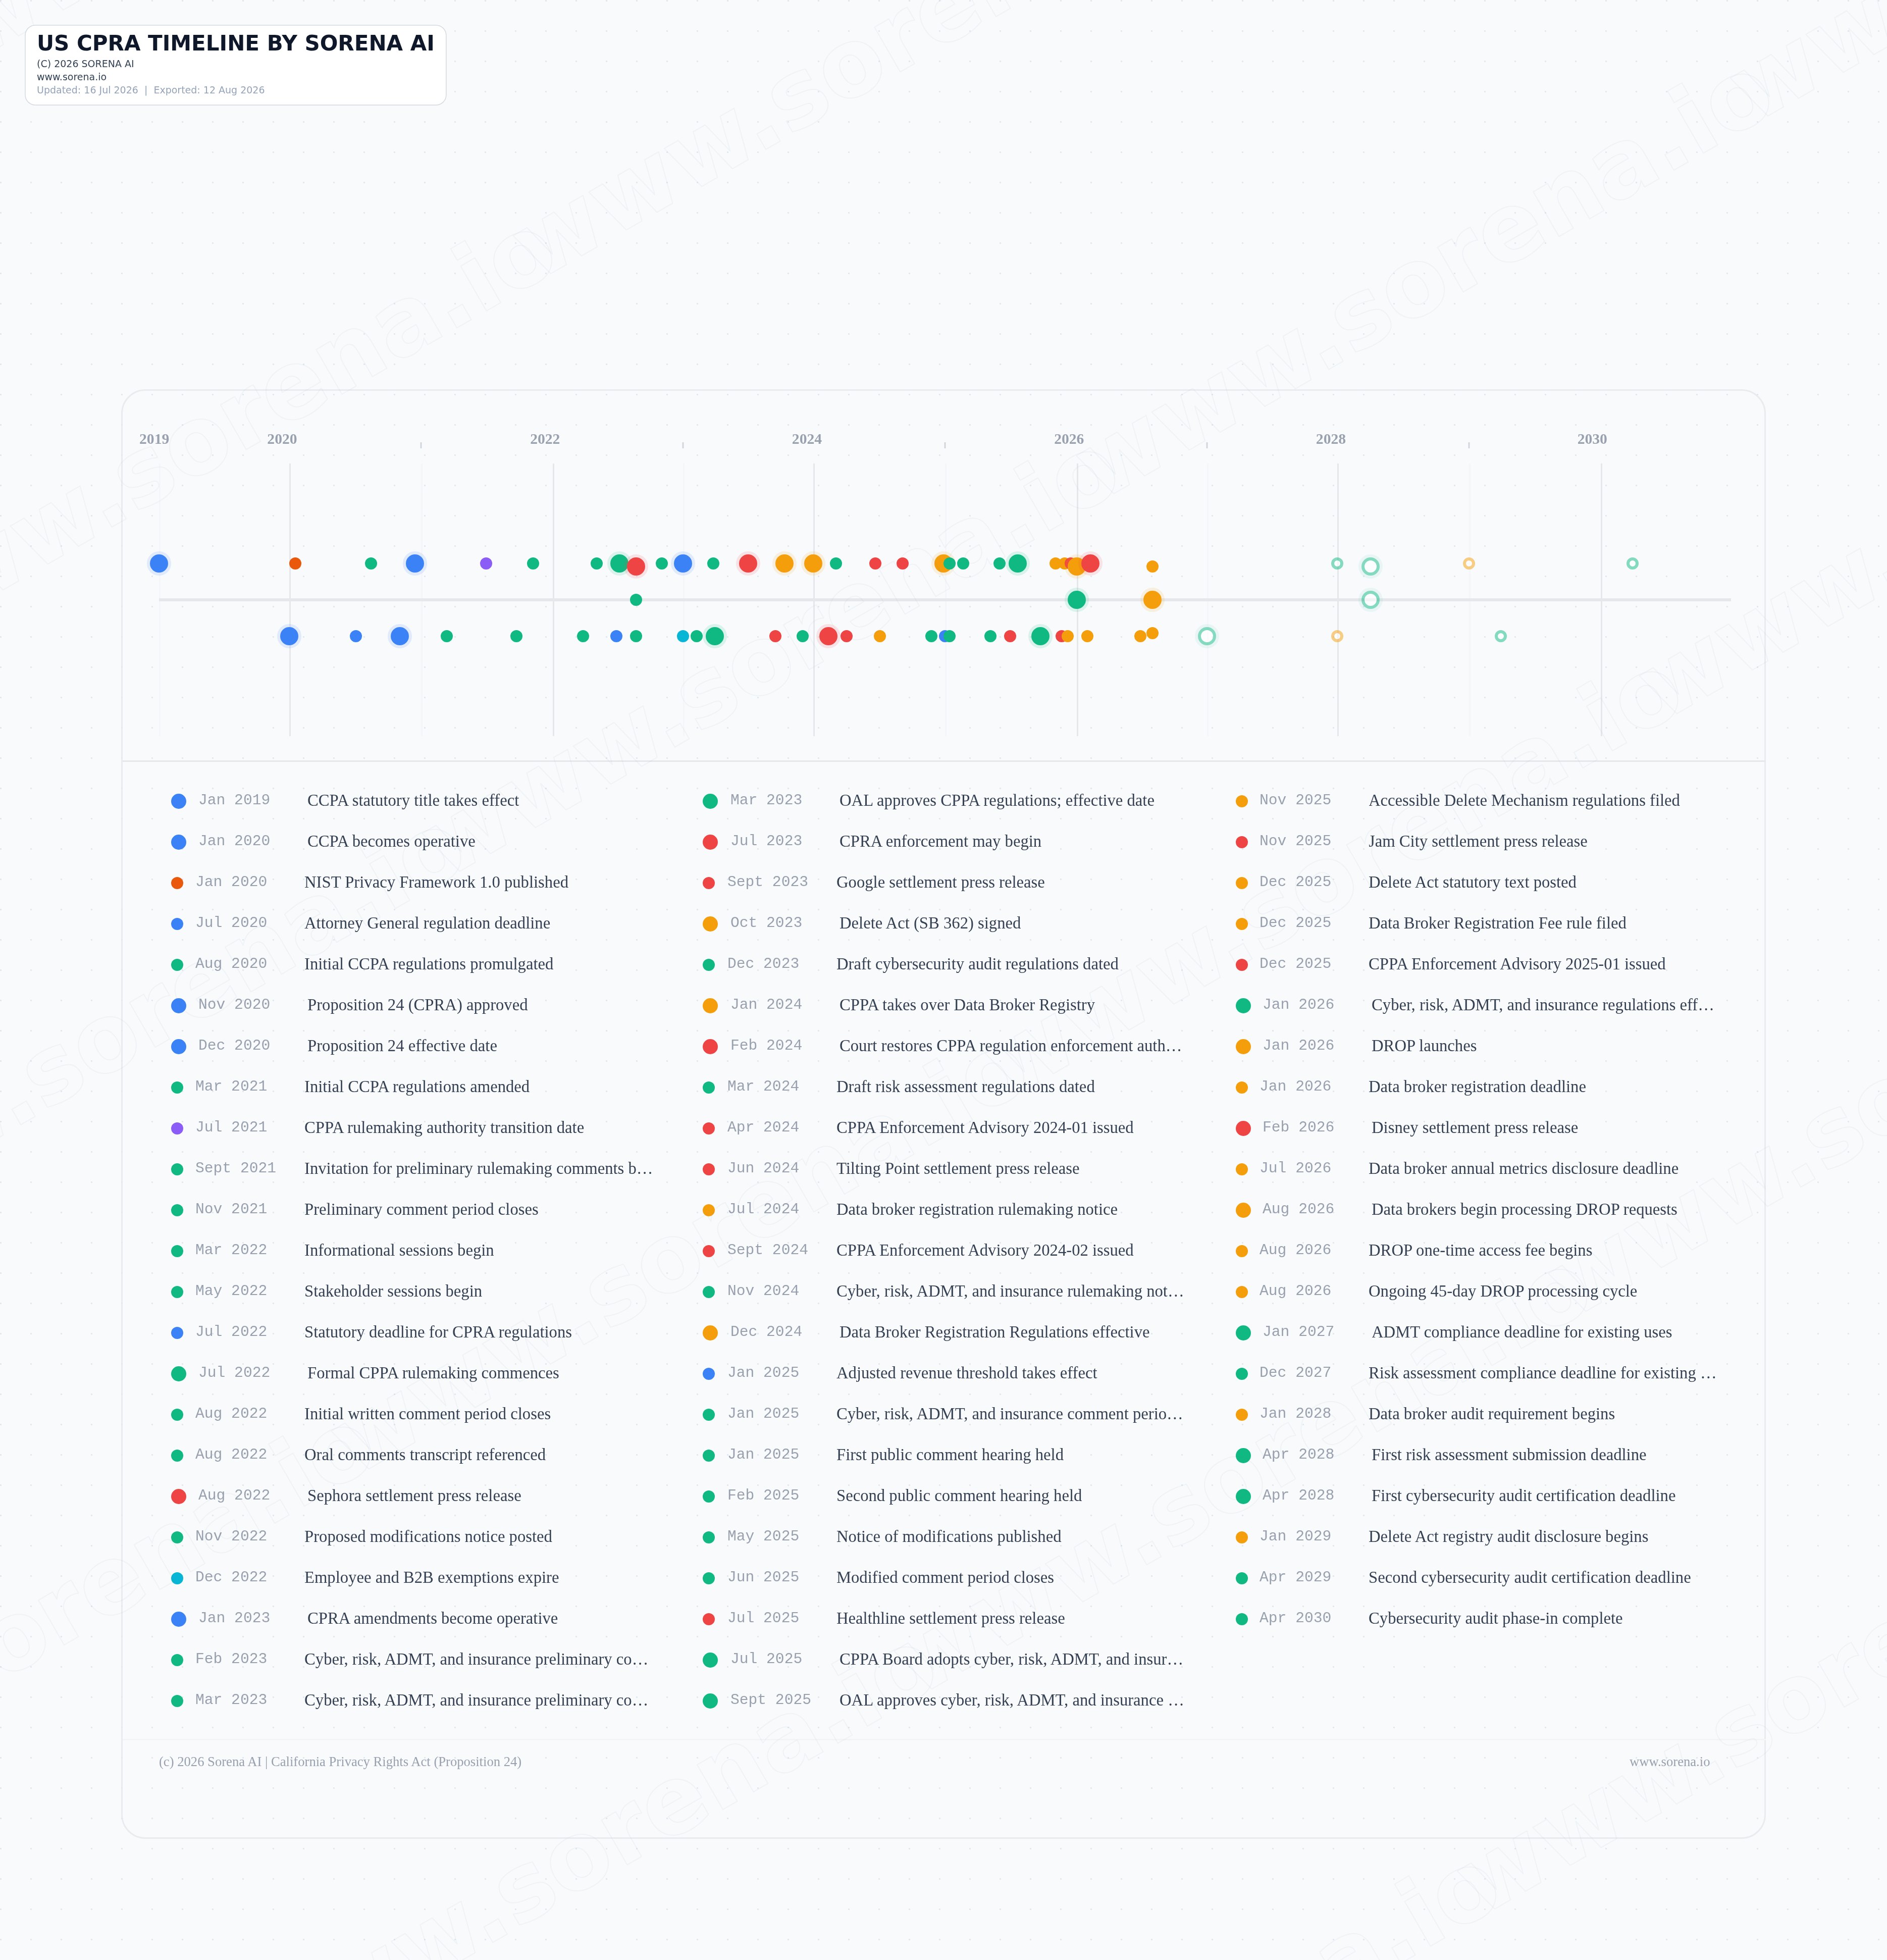
US CPRA Timeline and Implementation Guide
Apply the CPRA amendments within the CCPA framework, including scope, consumer rights, sensitive information, GPC, contracts, 2026 regulations, deadlines, and evidence.
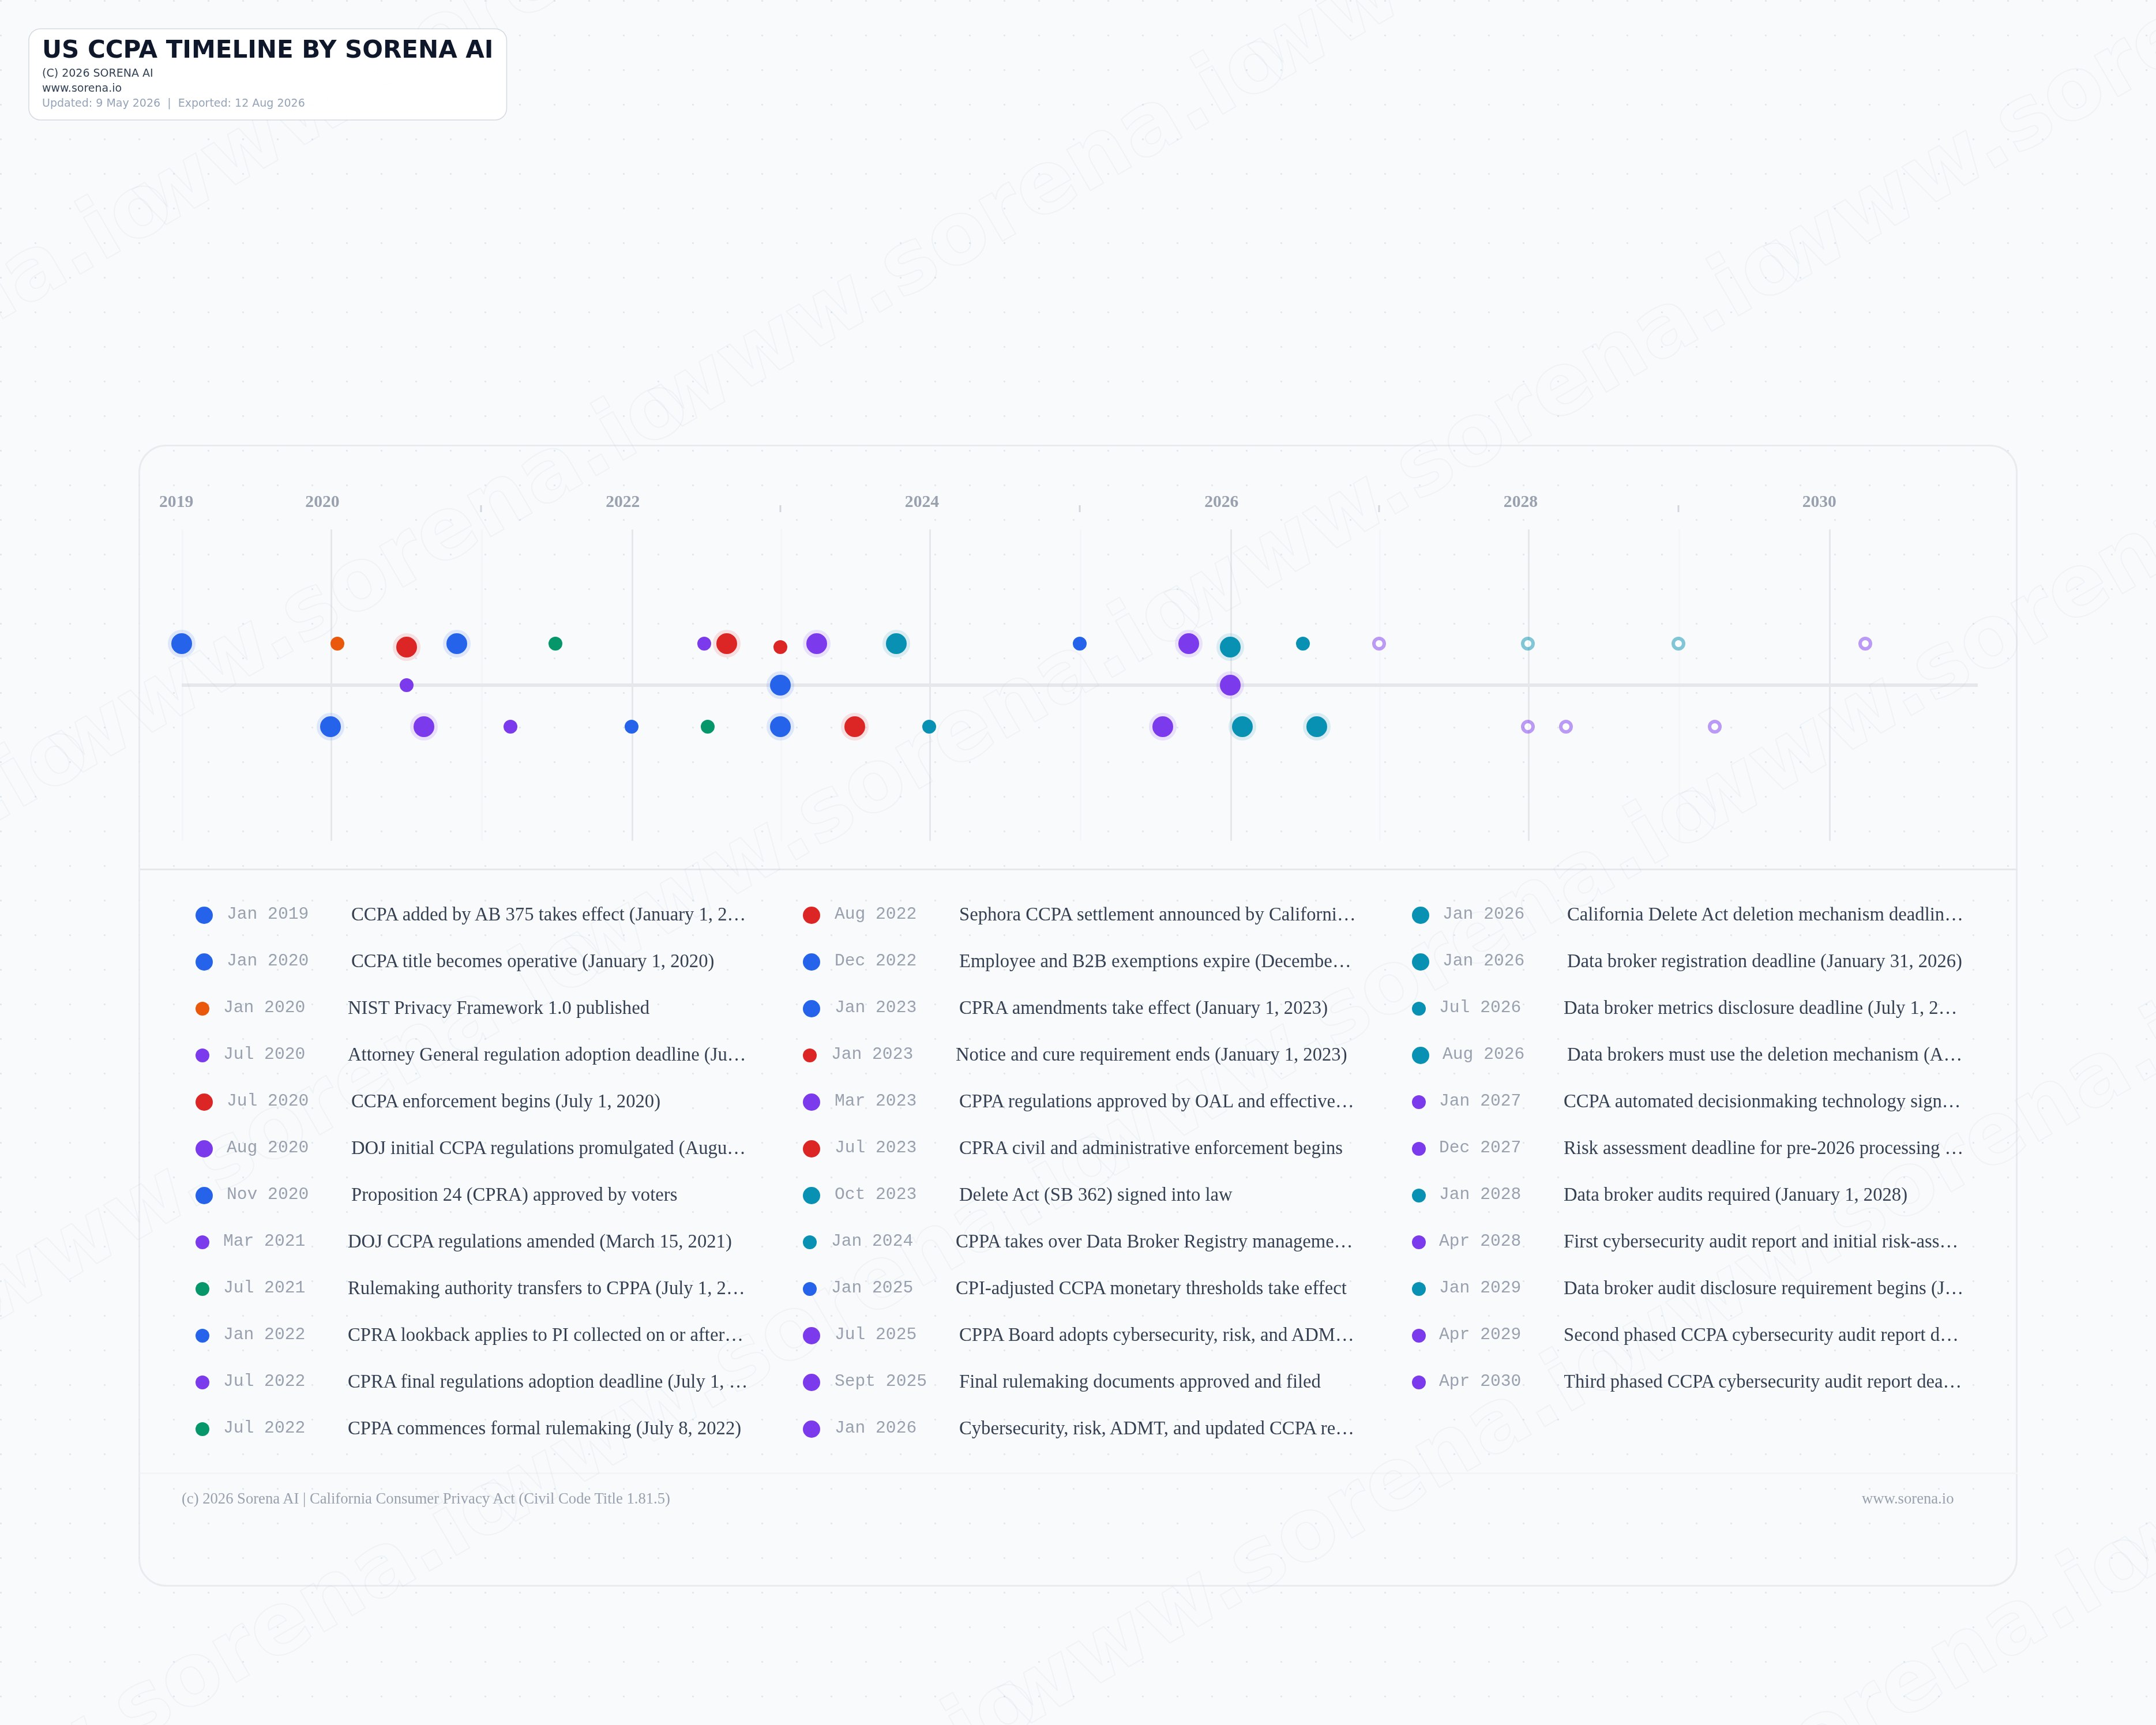
US CCPA Timeline and Implementation Guide
Apply the CCPA with its CPRA amendments and 2026 regulations, including scope, rights, GPC, contracts, risk assessments, cybersecurity audits, ADMT, data brokers, and enforcement.
Guidance tailored to your needs
Get guidance tailored to your organisation, systems, and deadlines, with specific actions for the teams responsible.
Talk to an expert